NOTE: Please refer to http://jboss.org/picketlink
==================================OUTDATED===========================
Please check: http://www.jboss.org/community/wiki/JBossIdentityFederation
for the most recent updates.
It gives me pleasure in announcing the next iteration of the JBoss Identity . The new version is 1.0.0.alpha2.
You can download the binary in zip format here for either JBoss Application Server or Apache Tomcat from here.
http://www.jboss.org/jbossidentity/downloads/
The documentation in zip format contains a User Guide as well as a Developer Guide.
What does this contain:
a) An IDM component (1.0.0.Alpha2) that has been driven by Bolek of JBoss Portal that provides an API/Model for your Identity needs in your applications.
b) Identity Federation component (v1.0.0.alpha2) that has the following:
- SAMLv2 based Web Browser SSO. (HTTP/Redirect Binding)
- SAMLv2 based Web Browser SSO with XML Signature Support.
- SAMLv2 based Web Browser SSO with XML Encryption Support.
c) Latest version of JBoss XACML component for Oasis XACML v2 support. (v2.0.3.CR1)
Developers who are interested in adding SAML support to their applications can use the API mentioned in the Developer guide.
All you need to do is unzip the distribution in JBAS or Tomcat. Please follow the User Guide for more information.
If you have any questions, please use the User Forum.
Please watch for more information on this wiki: http://www.jboss.org/community/docs/DOC-13254 (we will certainly provide more information here based on feedback).
Friday, February 27, 2009

Wednesday, February 25, 2009
IDTrust: Security in Java Applications
I have heard from folks who I have met face to face in the last few months that they need authentication, authorization and audit capabilities for their Java applications, when not running in a container such as JBoss AS. It also should be easy to port these applications to JBoss AS.
In this vein, I created a project sometime ago called as IDTrust but only recently released a jar out. You can use it in your stand alone applications (provided you download the dependent jars as mentioned in the wiki below).
You can get more info at this wiki page:
https://www.jboss.org/community/docs/DOC-13374
Please use the User Forum to communicate/critic it.
I know there is still work to be done from my end. Your feedback/questions will make the road smoother. :)
In this vein, I created a project sometime ago called as IDTrust but only recently released a jar out. You can use it in your stand alone applications (provided you download the dependent jars as mentioned in the wiki below).
You can get more info at this wiki page:
https://www.jboss.org/community/docs/DOC-13374
Please use the User Forum to communicate/critic it.
I know there is still work to be done from my end. Your feedback/questions will make the road smoother. :)
Wednesday, February 4, 2009
Kerberizing Web Identity and Services
Jeff Hodges blogs about some new work from MIT Kerberos Consortium.
You can look here.
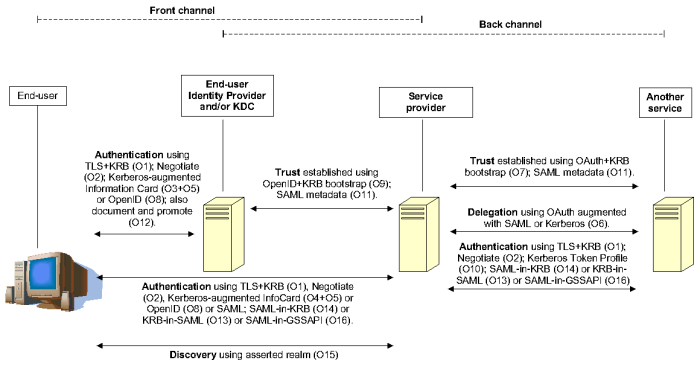
In my view, the span of Kerberos in terms of trust is limited to the footprint of the KDC. But this new proposal highlighted in this picture utilizes various other forms of trust identifiers to go along with Kerberos.
You can look here.
In my view, the span of Kerberos in terms of trust is limited to the footprint of the KDC. But this new proposal highlighted in this picture utilizes various other forms of trust identifiers to go along with Kerberos.
Subscribe to:
Posts (Atom)